About US
CyStrat Services GmbH — Managed Cyber Defense, Incident Response and Security Operations. Engineered in Germany, operated around the clock.
We are a specialist provider of managed security operations. Our team runs a Security Operations Center that detects, assesses and stops attacks together with our customers — technology-assisted, with a human analyst always making the call.
Management and leadership
The people running CyStrat Services and owning day-to-day operations — directly reachable, with no layers in between.
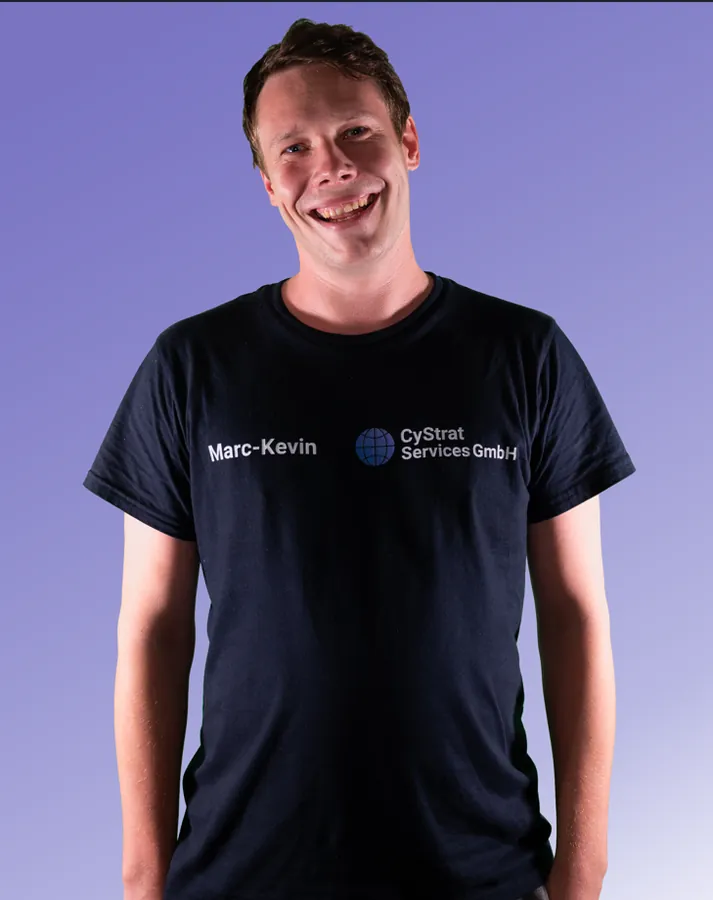
Marc-Kevin Lindner
Managing Director
Owns strategy, sales and back office — with roots in SIEM engineering and security operations.
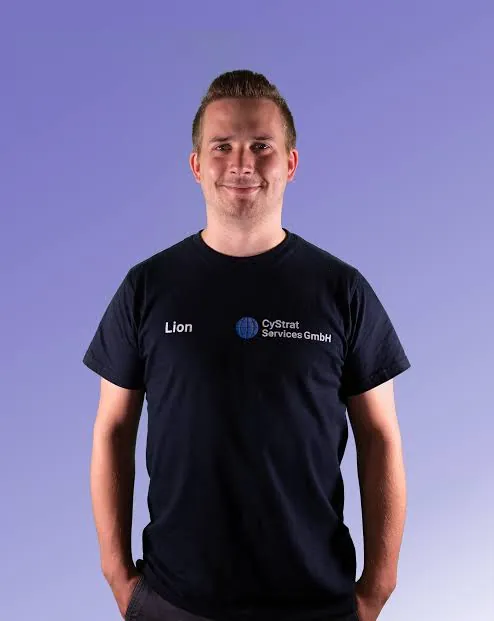
Lion Nagenrauft
Managing Director
Owns technology, services and the CyStrat SOC Suite platform as well as detection engineering and automation.
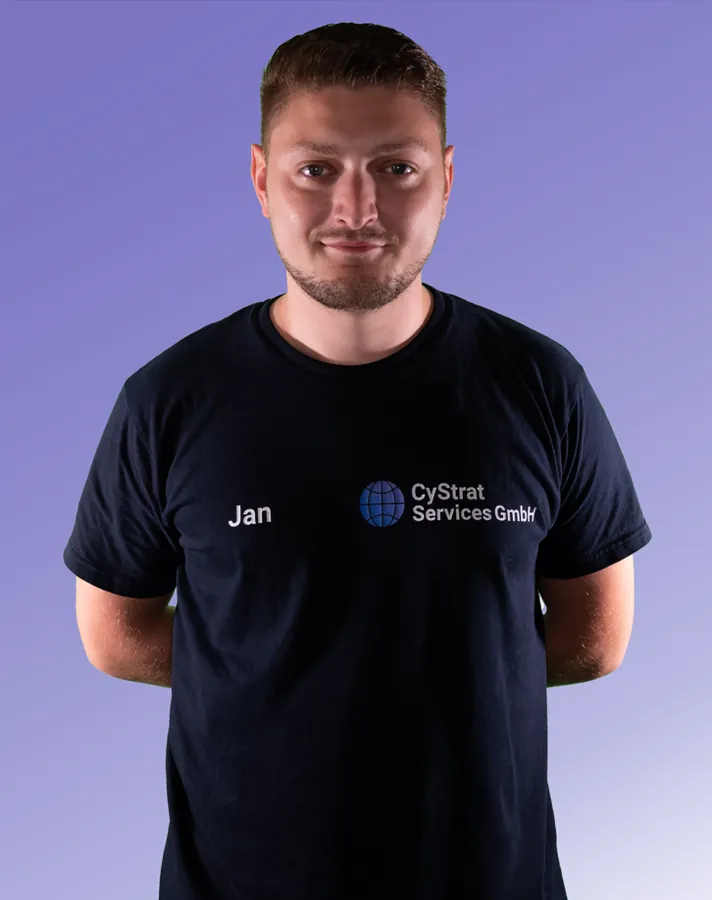
Jan Hallebach
Head of Analysis
Leads the analysis team in 24x7 operations: alert quality, triage standards and escalation into incident response.
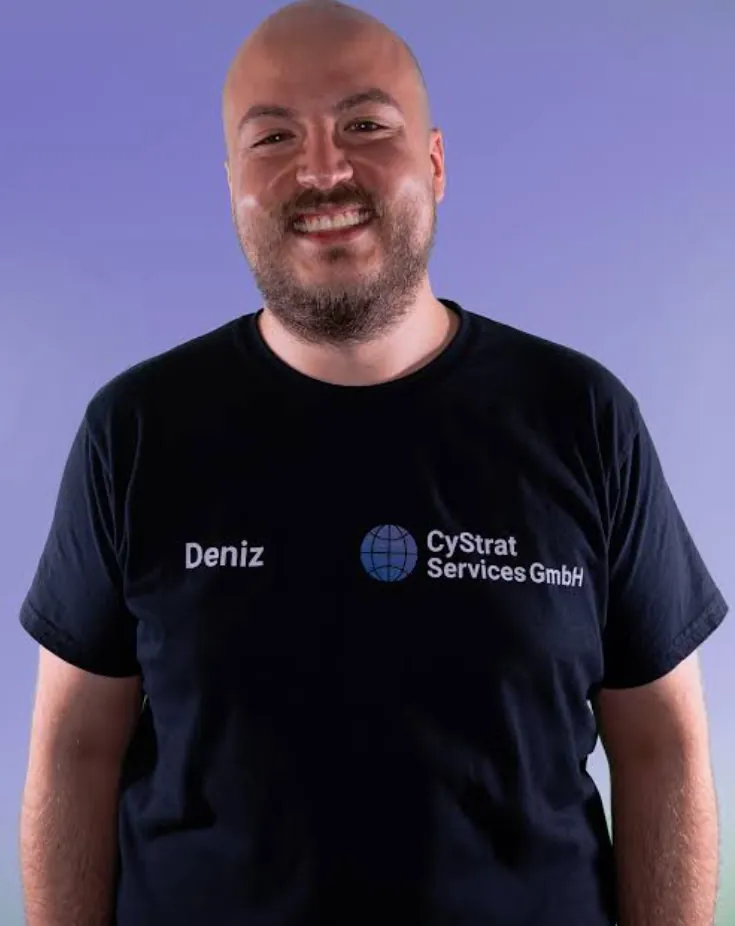
Deniz Ibicioglu
Head of Managed Service
Owns managed service delivery: onboarding, service quality, SLA adherence and day-to-day collaboration with customer teams.
Who we are
CyStrat Services GmbH, based in Maintal near Frankfurt am Main, grew out of practice: out of incident response engagements, out of SIEM projects, and out of one recurring observation — many organizations own security tooling, but nobody operates it around the clock.
That is the gap we close. We take over operations — as a fully managed SOC or as co-managed cyber defense alongside your team. From monitoring and SIEM through EDR operations, vulnerability management and SOAR automation to incident response, forensics and red teaming.
The company is led by Marc-Kevin Lindner and Lion Nagenrauft and registered at Hanau district court under HRB 98851.
- Managed and Co-Managed Cyber Defense (8x5 to 24x7x365)
- Incident Response and IT forensics
- SIEM consulting and use-case development
- Offensive security and security awareness
Company details
Our information security management system is certified against ISO/IEC 27001. What we ask of our customers applies to us first: audited processes, documented responsibilities and regular reviews.
Full provider information is available in the imprint.
What we stand for
Four principles every one of our services is measured against.
Technology assists, the analyst decides
Agentic AI and automation accelerate triage, enrichment and reporting. Any action inside your systems is always decided by an analyst.
Made in Germany
Infrastructure operations, data storage and points of contact in Germany — with clear contractual terms and GDPR-compliant processes. Analysis comes in different operating models: German-only service hours or follow the sun — in both cases the same permanently employed CyStrat Services GmbH team is on the case.
Transparency instead of a black box
You see what we see: use cases, alerts, metrics and decision paths are open in one platform.
A partnership, not a ticket desk
Dedicated analysts, joint reviews and a service scope shaped around your risk posture — not around our standard package.
How we work
A deliberately lean setup with clear ownership.
Team and culture
Our team combines SOC analytics, incident response, forensics, detection engineering and offensive security. We work in small, accountable units: whoever builds a detection also runs it in production — which shortens the path and keeps quality high.
- SOC analytics (L1–L3) and detection engineering
- Incident response and IT forensics
- SIEM and EDR engineering
- Offensive security together with partners
Partners
For parts of our offensive security work we cooperate with Exploit Labs GmbH — a specialist team for penetration testing and red teaming.
Contact
Get to know us
Whether managed SOC, co-managed cyber defense or an active incident — talk directly to our analysts.
Frequently asked questions
Answers to the questions our customers ask most often.
Who is behind CyStrat Services?
What sets CyStrat apart from large MSSPs?
Is CyStrat certified?
Do you work with smaller companies?
Question not answered here? Ask us