CyStrat
SOC Suite
Agentic all-in-one managed SOC: AI agents correlate signals from every module and support our analysts — response decisions stay with the human team.
Executive Summary
CyStrat SOC Suite v2 is the next-generation Security Operations Center platform designed for enterprise and MSSP environments. Built on a revolutionary AI-first architecture, it transforms security operations from reactive alert processing into proactive, intelligent threat hunting and response.
Single-Page Investigation
Complete alert analysis without module switching. Zero context switching.
AI-Powered Analysis
Every alert analyzed by AI agents with drilldown capability.
Sub-Minute Response
Automated playbook execution with AI recommendations in under 60 seconds.
Multi-Tenant Ready
Built for MSSP scale from day one. Global operations ready.
Agentic-AI Core
Every SOC module reports into the Agentic-AI orchestration core, which correlates and enriches signals and prepares response options. Automated playbooks only run inside limits you approve — anything beyond that is released by an analyst.
SIEM
Centralized Logging & Detection Foundation.
Explore module →
SOAR
Orchestration & Automated Response.
Explore module →
EDR Management
EDR context in the SIEM, response & audit-proof allow-listing.
Explore module →
Threat Intelligence
Threat Intel Aggregation & Operationalization.
Explore module →
Vulnerability Mgmt
Vulnerability Lifecycle: Scan to Remediation.
Explore module →
Compliance
Regulatory Reports & Audit Readiness.
Explore module →
COMPASS
Security & Risk Compass for Management.
Explore module →Core Platform Modules
Command Center
Executive Operations Dashboard
Real-time executive visibility into security operations. Non-technical executives get instant situational awareness.
- ✓ Global Threat Level Indicator with real-time scoring
- ✓ Active Incident Tracking & Time-to-resolution metrics
- ✓ Geographic Threat Distribution on interactive world map
- ✓ System Health Monitoring (CPU, Memory, Ingestion rates)
SIEM
Alert Management & Correlation
Centralized security event management with intelligent correlation. 95% noise reduction through AI filtering.
- ✓ 50,000+ events/second ingestion capability
- ✓ Real-time correlation & auto-deduplication
- ✓ Advanced filtering & custom views per analyst
- ✓ Behavioral correlation & kill chain mapping
Alert Detail
The Investigation Revolution
Single-page investigation platform with AI-powered analysis. Ask any question, get instant analysis.
- ✓ AI Analysis Agent with Executive Summary & Risk Scoring
- ✓ 17 Default Tabs + Dynamic AI-Generated Tabs
- ✓ Process Tree Visualization (D3.js)
- ✓ Full Audit Trail & Auto-generated incident reports
EDR
EDR context, response & audit
The module brings your existing EDR into the SIEM: detections and endpoint context next to network, cloud and identity data — with response and allow-listing from the same case.
- ✓ EDR detections and telemetry as SIEM context
- ✓ Active response such as host containment, analyst-decided
- ✓ Audit trail of privileged EDR response sessions
- ✓ Audit-proof allow-listing from the SIEM, depending on the EDR
Want the platform operated too? See EDR Operations & Response.
Threat Intelligence
Strategic Context & IOC Enrichment
Threat actor tracking and campaign monitoring mapped to MITRE ATT&CK. AI agents continuously enrich IOCs.
- ✓ 5,000+ threat actor database & campaign tracking
- ✓ VirusTotal integration & MISP feed ingestion
- ✓ MITRE ATT&CK Technique coverage heatmap
- ✓ Predictive analytics for next attack stages
Vulnerability Mgmt
Proactive Assessment & Patching
Continuous scanning, risk prioritization, and automated patch management. AI Risk Scoring prioritizes patches based on real threat intelligence.
- ✓ Continuous network & application scanning
- ✓ AI-based risk scoring & exploit availability tracking
- ✓ Automated patch deployment & rollback capability
- ✓ Compliance mapping (PCI-DSS, ISO 27001)
SOAR
Orchestration & Automation
Automated response playbook execution. Sub-60-second execution times. AI suggests optimal playbooks per alert.
- ✓ Visual Playbook Designer with 200+ pre-built playbooks
- ✓ 500+ security tool integrations
- ✓ Self-Healing AI agents fix playbook failures
- ✓ Automated response faster than manual triage
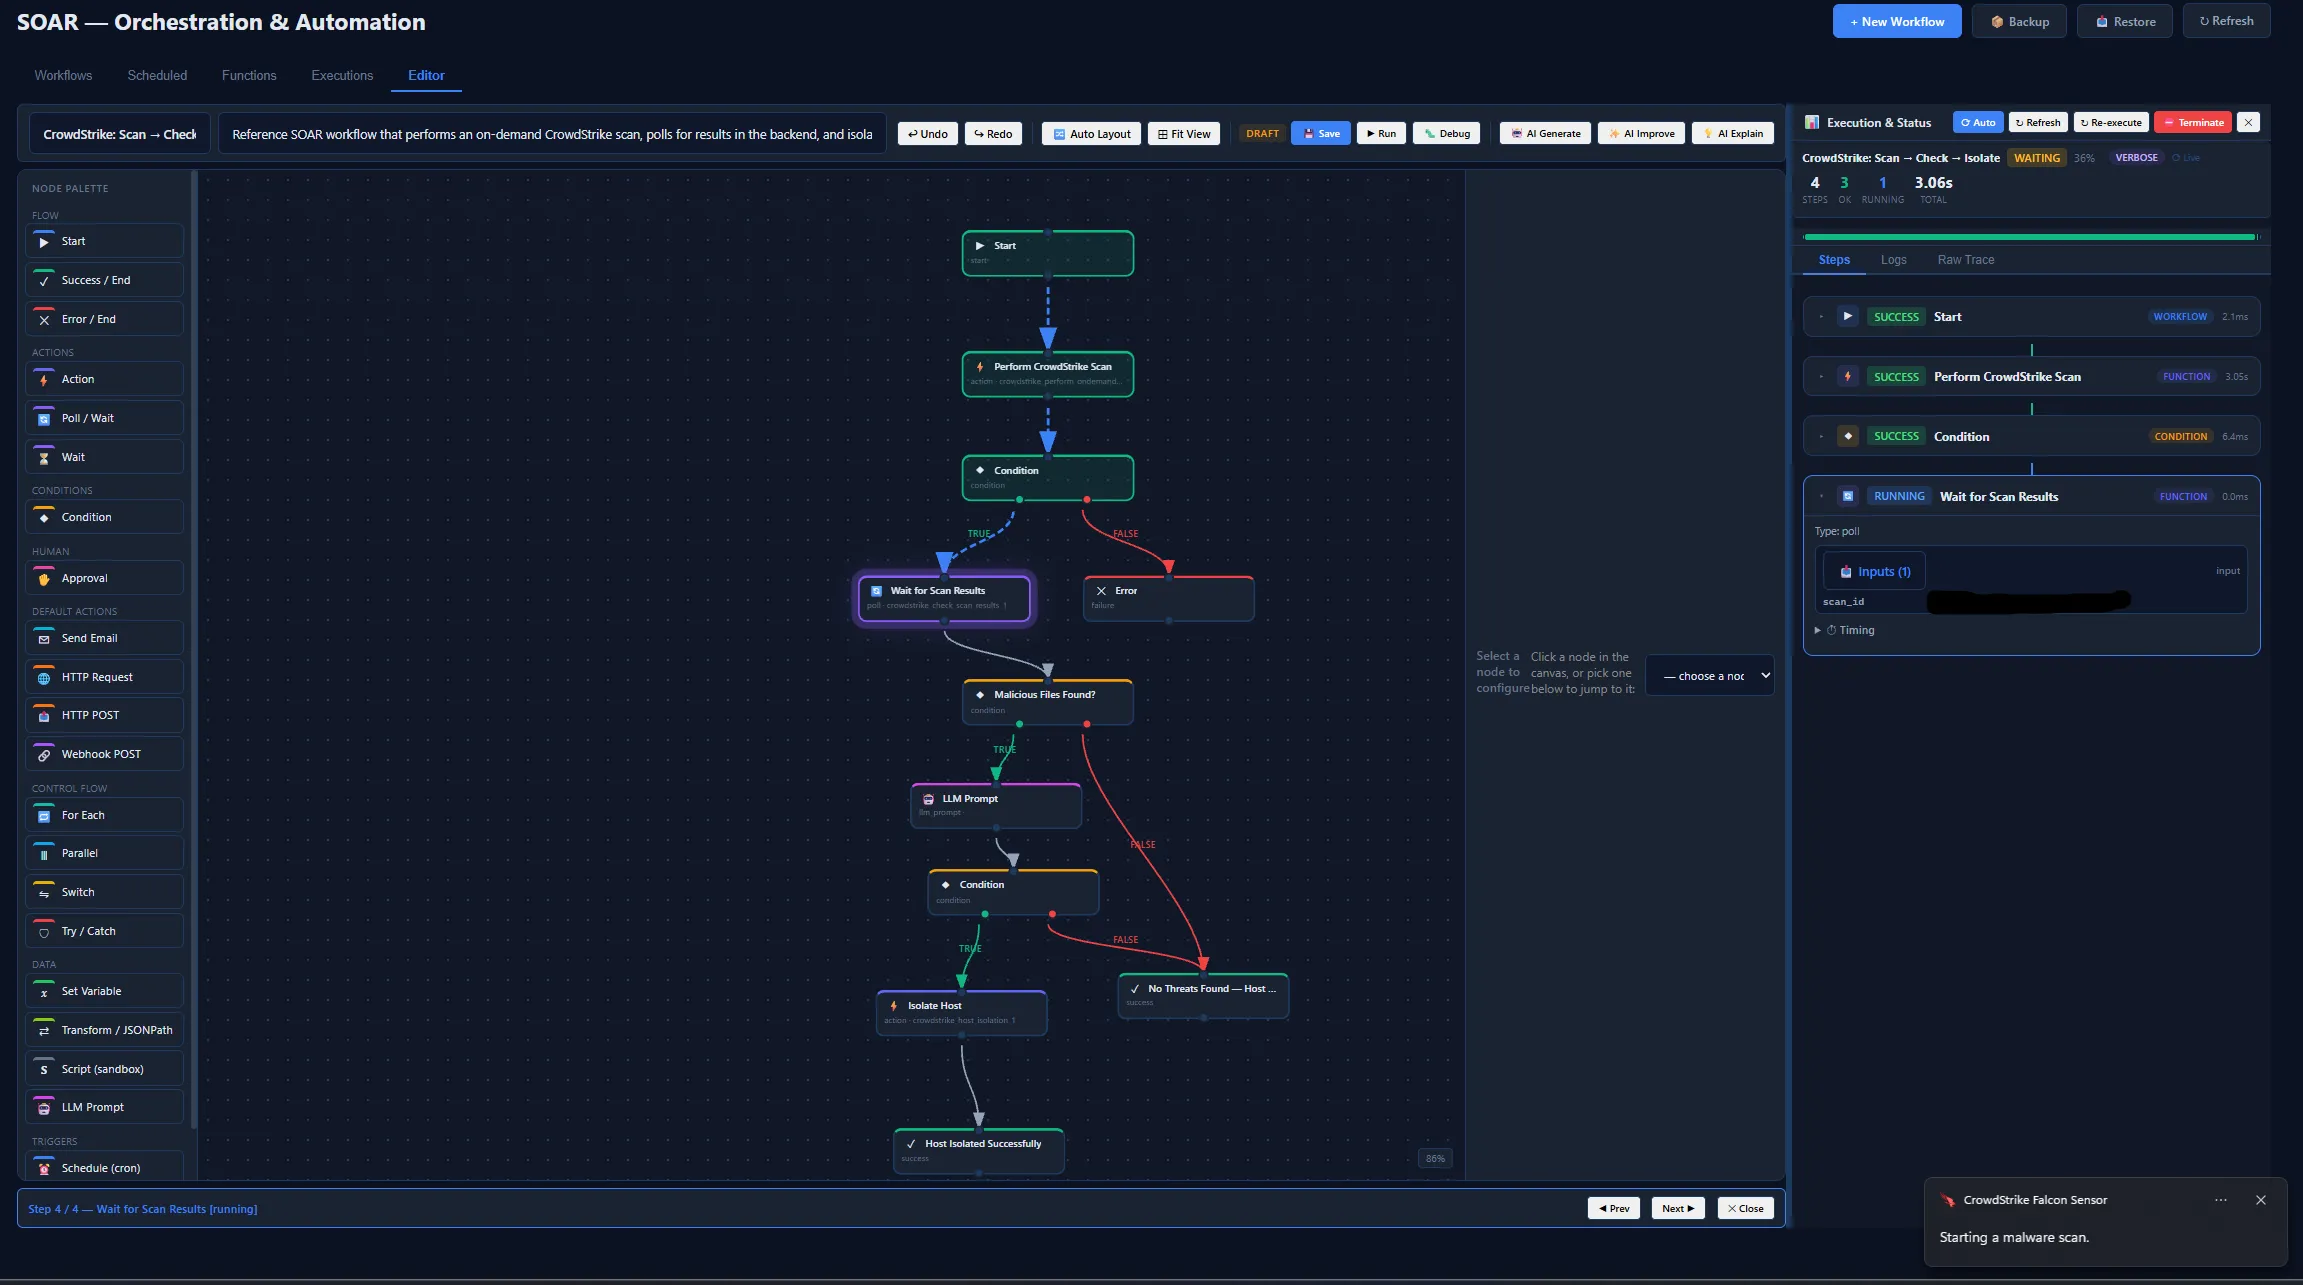 Click to enlarge
Frequently asked questions
Answers to the questions our customers ask most often.
Which modules does the SOC Suite include?
Where is the data stored?
How long are logs retained?
Can the suite run on-premises?
Question not answered here? Ask us